


Where frontier AI meets security and the experts behind it
Not a model lab. Not a traditional security research team.
AI labs
World-class models and compute.
Security research
Deep domain expertise and operational data.

Frontier Cyber AI Lab
Publishing what we learn so the whole field can use it.
The team
AI and security researchers working side by side, combining deep AI knowledge with hard-won security experience.
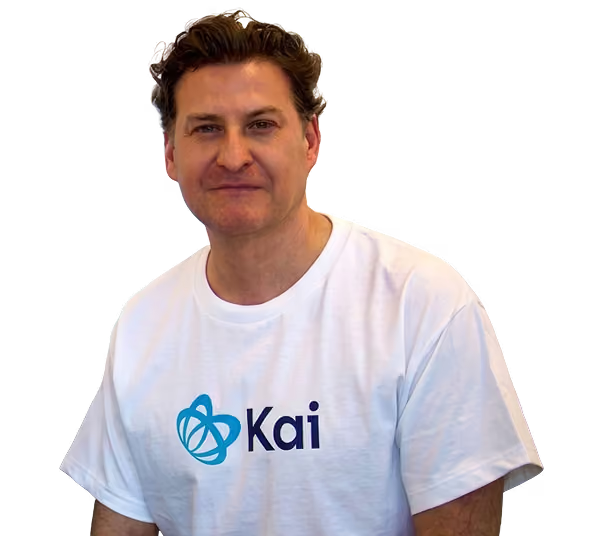
Damiano Bolzoni, PhD
Co-founder & CTO
A serial security founder. After building SecurityMatters into a company acquired by Forescout, he co-founded Kai to bring AI to the hardest problems in security.
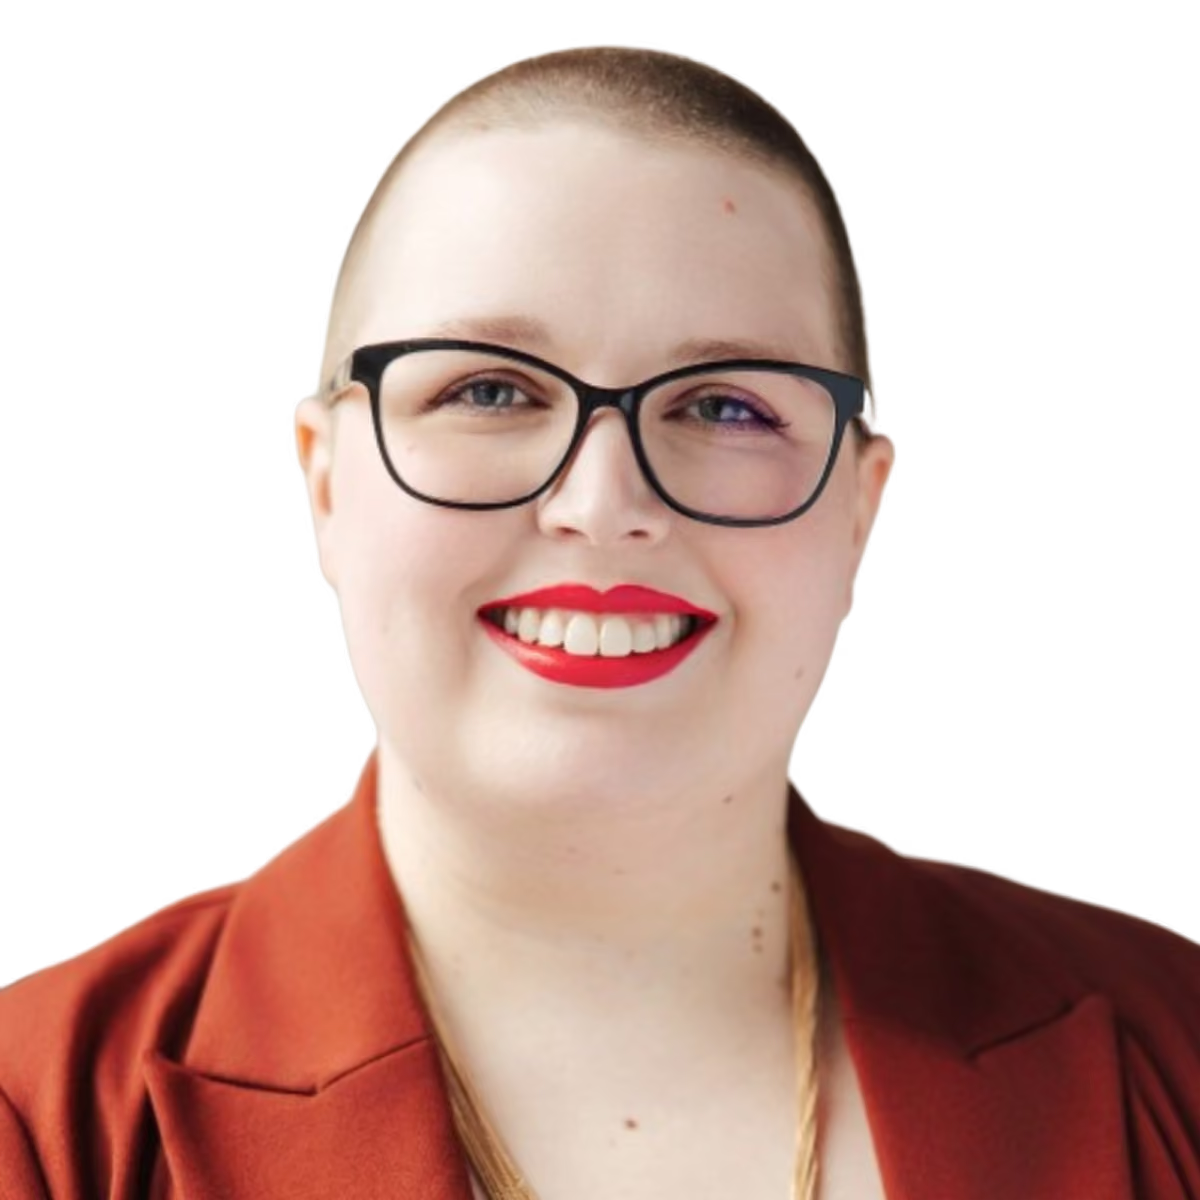
Kylie McClanahan, PhD
Research Director
Nearly a decade in the electric utility sector, a PhD in Computer Science, and a GCIP certification, the only certification for the NERC CIP standards.
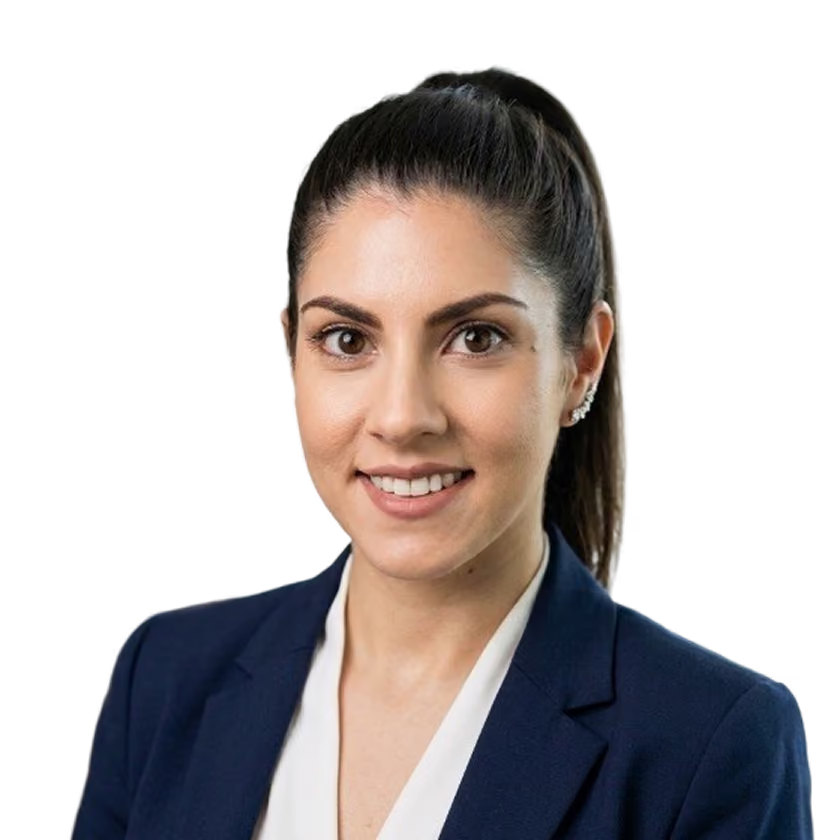
Maria Kissa, PhD
Principal AI Scientist
A decade building production ML and GenAI systems, with patents in graph neural networks and language models. Doctorate in biomedical text mining.
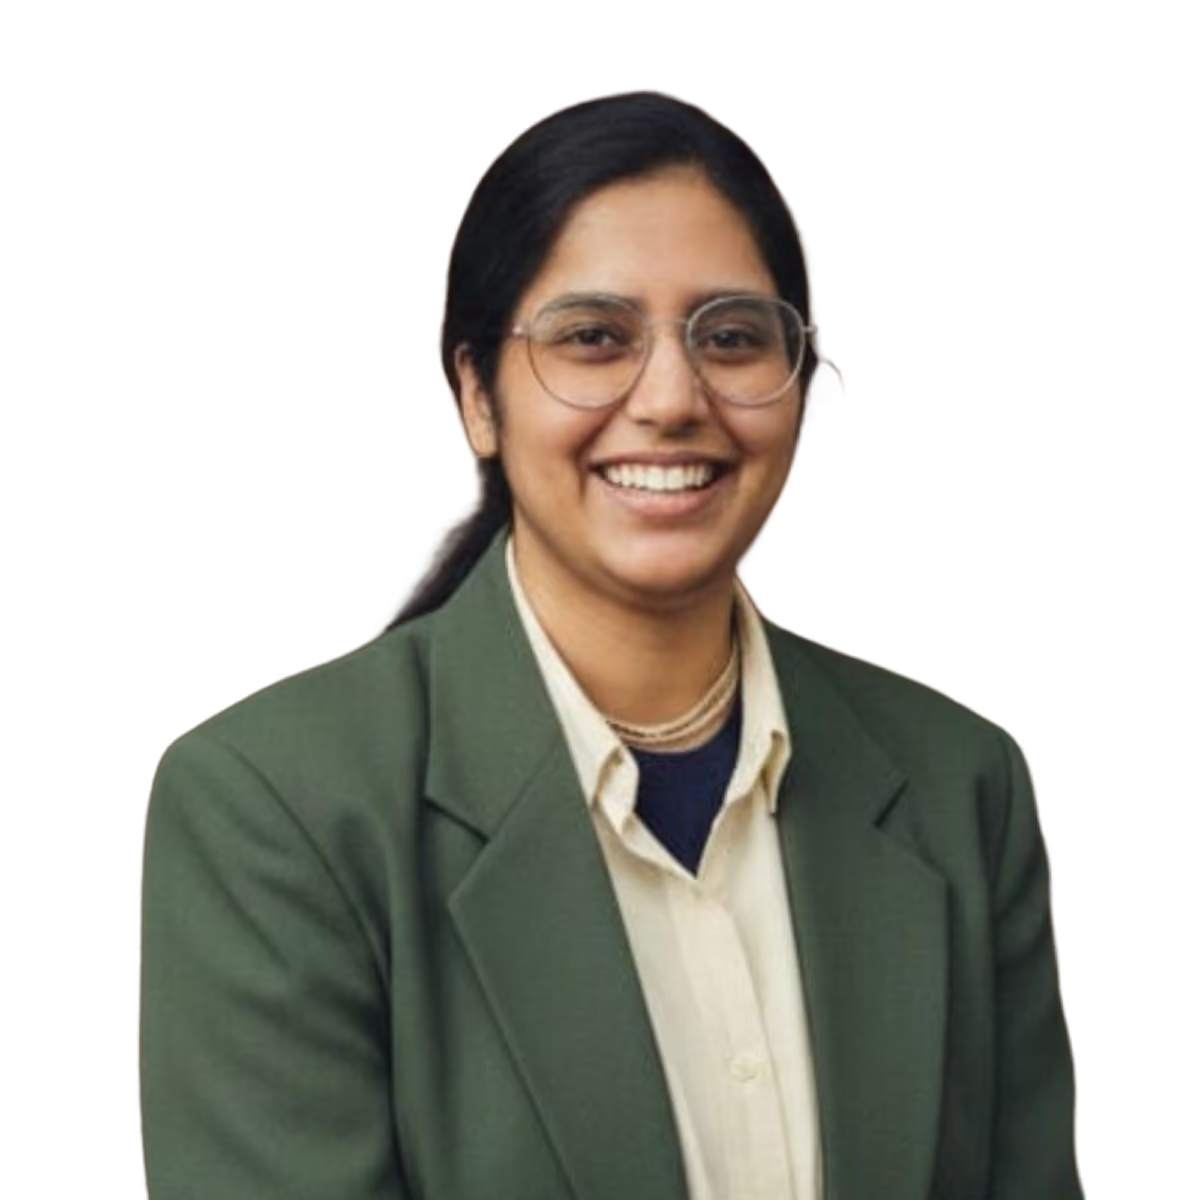
Shravya Kanchi, PhD
Applied AI Scientist
Completed a PhD in AI security and now works on putting those techniques into production rather than leaving them in papers.
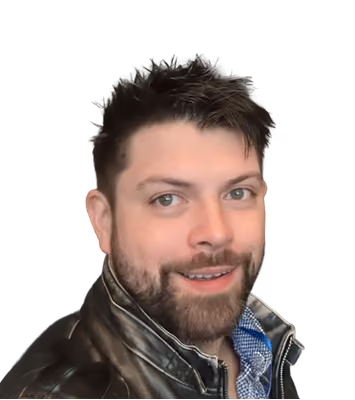
Ian Hanley
Security Researcher
Author of three books on Microsoft XDR, KQL and PowerShell. His detection work asks why a syntactically valid query can still return a misleading answer.
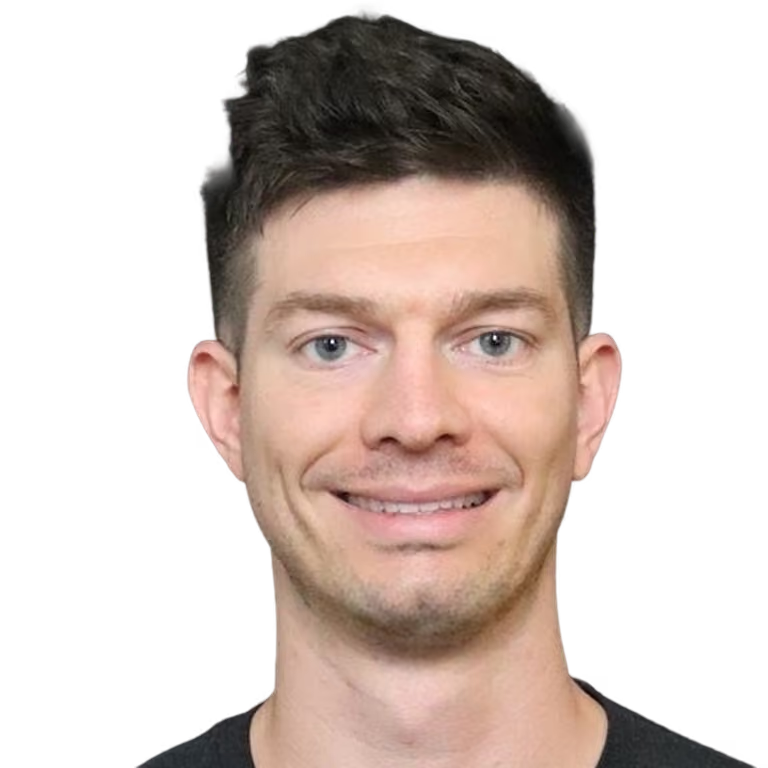
Kevin Cooper
Security Researcher
Application security and vulnerability management, with a focus on DAST and SAST. OSWE-certified, competes in CTFs, and contributes to open-source security tooling.
Tyler Webb
Security Researcher
Focuses on offensive security research, building automation that lets that work run at scale. He brings experience from both enterprise application security and fast-moving startups.
Tejas Nikam
Security Researcher
A security researcher with over ten years of experience building detection and response programs at Fortune 500 companies and startups. He focuses on threat intelligence and hunting, using LLMs.
Mason Moreland
Security Researcher
A security researcher specializing in red teaming and offensive security for AI-driven systems. He spent five years at SentinelOne building its vulnerability program and red-teaming its AI.
Research pillars
Shifting the balance back toward defenders.

Patents
Vulnerability management, application security, autonomous remediation, and autonomous triage.

Offensive learning
Learn from the attacker.
Defending efficiently means exploring the whole attack space. That’s why we run AI as the attacker against realistic targets to learn what it can really do, then turn each technique into defense: exploit validation, detection rules, and attack-path analysis.

Autonomous action
Taking actions with trust.
We research how AI can generate the right fix, predict its impact before it runs, and land it in the owner’s existing workflow and change windows.

Decision models
Models that decide, not just write.
Security work is mostly comprised of repeated decisions: is this exploit real, how severe is the vulnerability, is this code safe to run? We build small, calibrated decision models that answer with a confidence you can set thresholds on, fast enough to run on every commit.

Trusted autonomy
Make autonomy safe to trust.
Autonomy only scales if leaders can trust it. We don’t trust what we haven't tried to break ourselves, so we attack Kai’s own guardrails (the action boundary, isolated validation, the audit trail) and red-team the AI agents that defenders rely on.

Security context
Know what you own, and who owns it.
You can’t fix what you aren’t aware of, so every decision downstream depends on the asset record being right. We research how AI agents can query CMDB, endpoint, cloud, identity, scanning, and code systems, then rebuild each record from evidence: owner, environment, business application, and coverage.
Our methodology
How we turn open questions into evidence.
01
Scope
Day 0
We define the target environment, goals, measured variables, and expected outcomes before any model runs.
02
Attack
Full chain
We run AI agents and human-plus-AI red teams through our scenario as-defined in isolated, instrumented ranges—watching closely for anomalous behavior.
03
Evaluate
Metrics matter
Different experiments require different measurements. We aim to evaluate on four primary axes: time, cost, scale, and effectiveness.
04
Iterate
Spark ideas
We learn from every engagement. We take what we've observed and use it to inform future directions.
05
Publish
Go public
We publish our findings responsibly. We engage with the broader security community through conference talks, peer-reviewed papers, blogs, and more.



© 2026 Kai Cyber Inc. All rights reserved.
90 Skyport Drive, Suite 200 San Jose, CA 95110