

Every asset owned. Every gap surfaced.
Fixes stall when nobody owns the asset
You have an endpoint tool, a scanner, a cloud posture tool and a CMDB, assuming each holds your asset inventory, but none of these sources agree. A finding without an accountable owner goes to the nearest queue, is reassigned once or twice, and eventually ages out into obscurity.
of CISOs already let machines discover and inventory assets without approval.
Source: Kai, 2026 State of Autonomous Defense Report. Wakefield Research survey of 500 security leaders at $500M+ organizations, June 2026.
Every finding reaches the person who can fix it, the first time
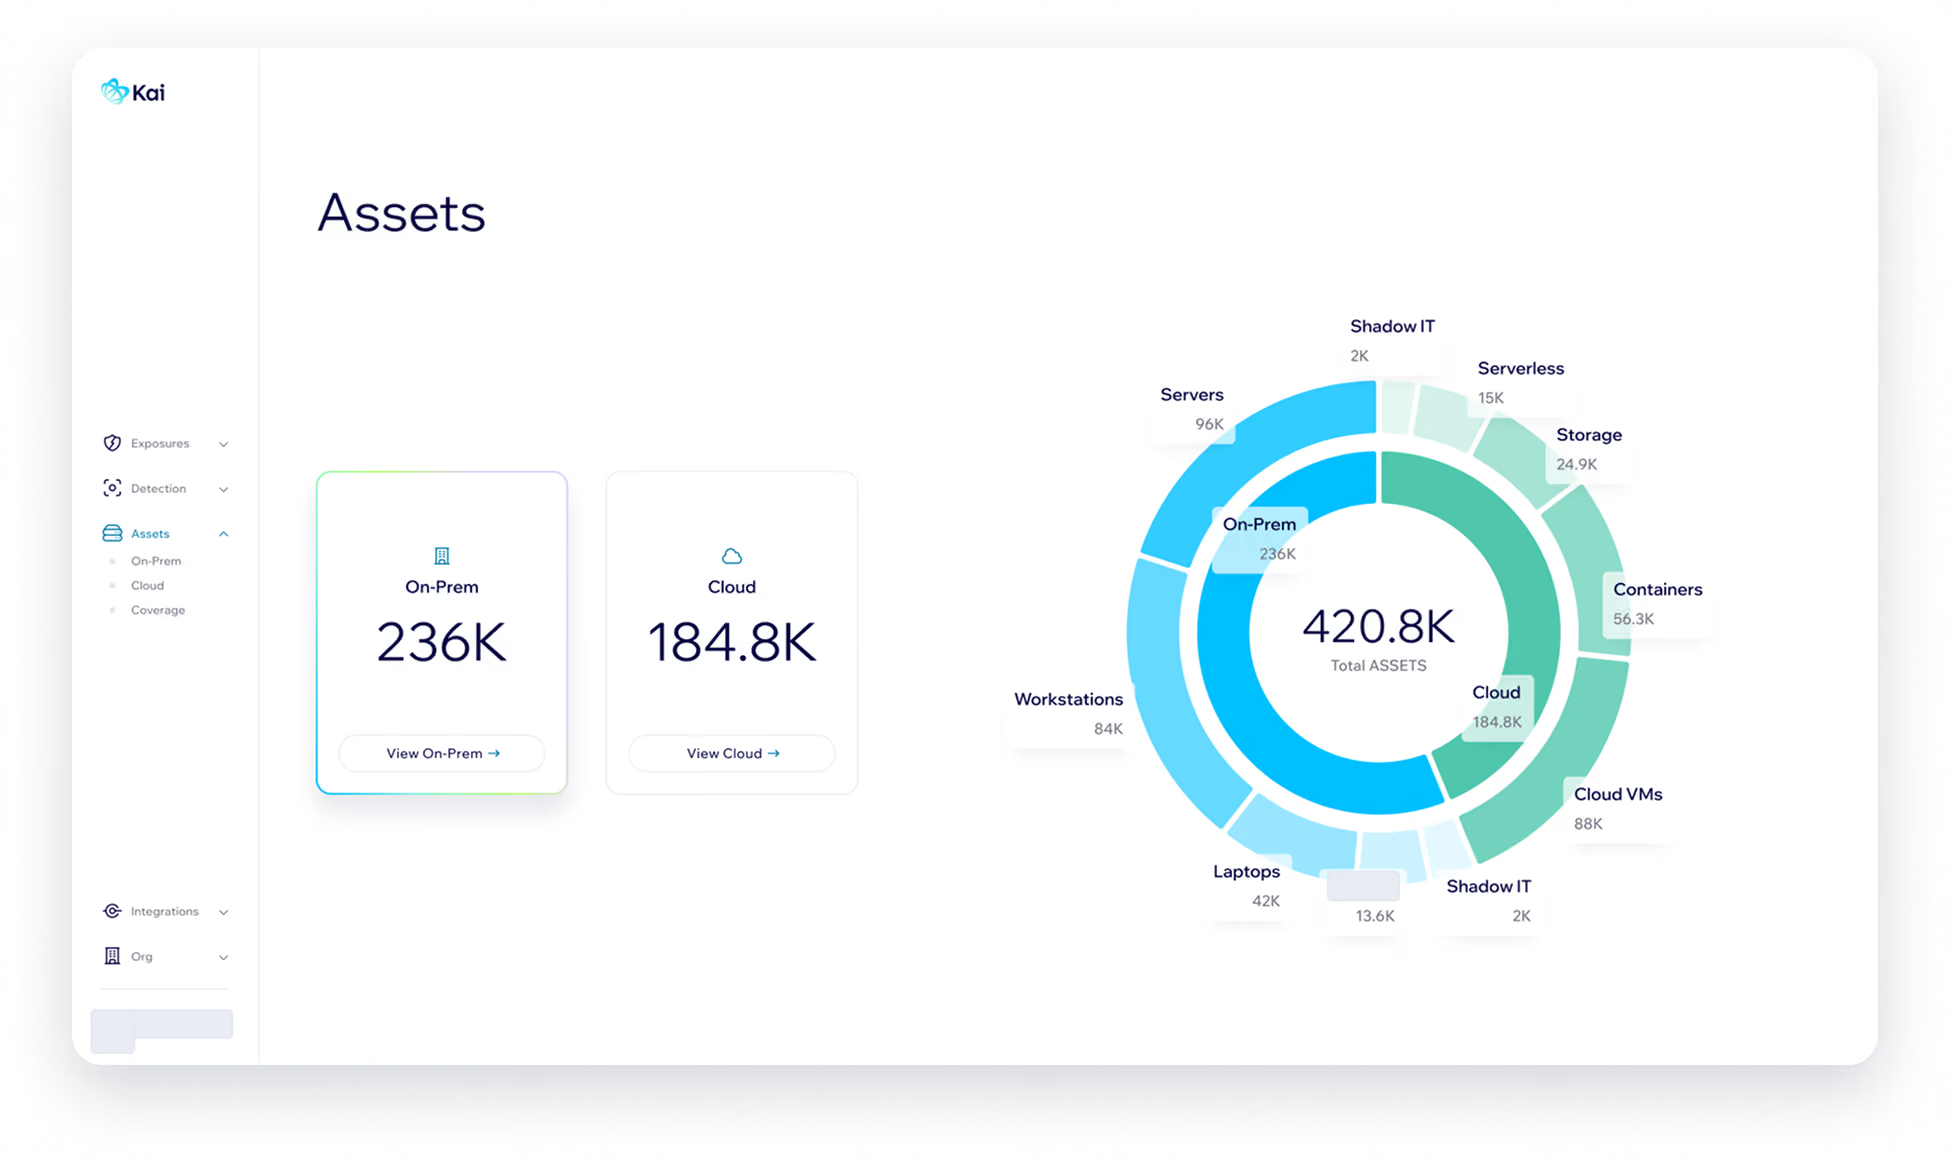
Kai rebuilds each asset from evidence across your tools and names the accountable owner, so every fix routes the first time.

Each asset rebuilt from Intune, Entra ID, EDR, scanners, cloud and CMDB
Missing EDR or scanner coverage raised as a finding
End of life software flagged with time to plan the upgrade
Owner, business application and environment named on every finding
Shadow assets returned to EDR and scanning coverage
Nothing waits on the CMDB being correct first
Know who owns every asset, without cleaning the CMDB first
1
2
3
4
Seven systems. Seven inventories.

Owner fields

Agents, unmanaged assets

Resource tags, inconsistently applied

Who actually logs in

What each one can reach

Repositories and pipelines

Patch management, change tickets
Interrogated, not reconciled.
Every source, every field, with its timestamp. Nothing is nominated as the system of record.
Last login, ticket history and cloud tags corroborate the record or overrule it.
Where sources are silent or disagree, the answer says so rather than posing as a fact.
One row per asset, rebuilt.

The accountable team, corroborated

Production, development, test

And the unit that pays for it

Agent present, scanner reach

End of life and end of support / SBOM with lead time
From four inventories to one answer IT and Security trust

Four partial inventories with no shared identity
Owners chased by hand, ticket by ticket
One or two reassignments per ticket
Coverage numbers nobody trusts
One asset record, rebuilt from evidence
An accountable owner on every finding
Fixes that route to the right team the first time
Coverage gaps raised as findings
Ownership from 4% to 92% in under twelve hours
Kai rebuilt 250,000 assets from the evidence in the company’s existing tools and surfaced 30,000 assets its EDR had marked unmanaged.

From the configuration record
Configuration record, cloud tags as fallback
Cloud region tag, no record to confirm it
Corroborated by who has been logging in and who has been receiving the tickets. Where sources conflict, the inference is labeled rather than promoted to a fact.
Ownership coverage, under twelve hours
An inventory you can defend in any audit

Frequently asked questions
Where does the asset record come from?
Kai reads the inventories you already run, including the CMDB, endpoint management, vulnerability scanners, cloud posture, identity and source control, and rebuilds each asset from the evidence they hold rather than trusting a single system of record.
How is ownership resolved?
In three tiers: business application, business unit and location, corroborated by login and ticket history. At a Fortune 50 energy company this took ownership coverage from 4% to 92% across 250,000 assets in under twelve hours.
What about the assets nobody knew about?
The same engagement surfaced 30,000 assets that endpoint tooling had marked unmanaged. Kai returns them to EDR and scanning coverage and flags end-of-life software with enough lead time to plan the upgrade.
Why does this matter for remediation?
Every downstream decision depends on the owner, the environment and the business application being right. With the record rebuilt from evidence, fixes route to the right team first time, priorities match the business, and nothing is worked twice.


